


• bitcoinBitcoin(BTC)$65,081.001.08%
  • ethereumEthereum(ETH)$1,822.092.89%
  • tetherTether(USDT)$1.000.01%
  • binancecoinBNB(BNB)$594.262.99%
  • usd-coinUSDC(USDC)$1.000.01%
  • rippleXRP(XRP)$0.976.30%
  • solanaSolana(SOL)$72.023.16%
  • tronTRON(TRX)$0.305219-0.78%
  • Figure HelocFigure Heloc(FIGR_HELOC)$1.061.03%
  • HyperliquidHyperliquid(HYPE)$67.838.48%
  • zcashZcash(ZEC)$905.868.60%
  • moneroMonero(XMR)$494.694.67%
  • dogecoinDogecoin(DOGE)$0.0590643.97%
  • USDSUSDS(USDS)$1.000.03%
  • leo-tokenLEO Token(LEO)$9.13-0.20%
  • whitebitWhiteBIT Coin(WBT)$63.010.87%
  • chainlinkChainlink(LINK)$9.275.80%
  • cardanoCardano(ADA)$0.1540794.60%
  • stellarStellar(XLM)$0.1402525.45%
  • Ethena USDeEthena USDe(USDE)$1.000.01%
  • daiDai(DAI)$1.000.02%
  • bitcoin-cashBitcoin Cash(BCH)$208.873.95%
  • nearNEAR Protocol(NEAR)$3.187.66%
  • litecoinLitecoin(LTC)$45.402.60%
  • CantonCanton(CC)$0.0832717.86%
  • avalanche-2Avalanche(AVAX)$7.292.81%
  • uniswapUniswap(UNI)$5.168.91%
  • tether-goldTether Gold(XAUT)$3,838.791.49%
  • USD1USD1(USD1)$1.000.04%
  • suiSui(SUI)$0.735.70%
  • the-open-networkGram (prev. Toncoin)(GRAM)$1.051.96%
  • Ripple USDRipple USD(RLUSD)$1.000.00%
  • Global DollarGlobal Dollar(USDG)$1.00-0.02%
  • paypal-usdPayPal USD(PYUSD)$1.000.03%
  • hedera-hashgraphHedera(HBAR)$0.0591095.37%
  • RainRain(RAIN)$0.003476-3.80%
  • Ondo US Dollar YieldOndo US Dollar Yield(USDY)$1.150.00%
  • shiba-inuShiba Inu(SHIB)$0.0000044.09%
  • BittensorBittensor(TAO)$193.165.70%
  • quant-networkQuant(QNT)$154.778.49%
  • crypto-com-chainCronos(CRO)$0.0430450.84%
  • Circle USYCCircle USYC(USYC)$1.140.00%
  • Spiko Amundi Overnight Swap Fund (EUR)Spiko Amundi Overnight Swap Fund (EUR)(EURSAFO)$1.120.04%
  • MemeCoreMemeCore(M)$0.845.46%
  • okbOKB(OKB)$88.164.43%
  • pax-goldPAX Gold(PAXG)$3,842.461.59%
  • aaveAave(AAVE)$109.389.88%
  • Falcon USDFalcon USD(USDF)$1.000.15%
  • BlackRock USD Institutional Digital Liquidity FundBlackRock USD Institutional Digital Liquidity Fund(BUIDL)$1.000.00%
  • United StablesUnited Stables(U)$1.000.02%
TradePoint.io
  • Main
  • AI & Technology
  • Stock Charts
  • Market & News
  • Business
  • Finance Tips
  • Trade Tube
  • Blog
  • Shop
No Result
View All Result
TradePoint.io
No Result
View All Result

Evaluating AI Model Security Using Red Teaming Approach: A Comprehensive Study on LLM and MLLM Robustness Against Jailbreak Attacks and Future Improvements

April 7, 2024
in AI & Technology
Reading Time: 5 mins read
A A
Evaluating AI Model Security Using Red Teaming Approach: A Comprehensive Study on LLM and MLLM Robustness Against Jailbreak Attacks and Future Improvements
ShareShareShareShareShare

The emergence of Large Language Models (LLMs) and Multimodal Large Language Models (MLLMs) represents a significant leap forward in AI capabilities. These models have advanced to a point where they can generate text, interpret images, and even understand complex multimodal inputs with sophistication that closely mimics human intelligence. However, as the capabilities of these models have expanded, so too have the concerns regarding their potential misuse. A particular concern is their vulnerability to jailbreak attacks, where malicious inputs can trick the models into generating harmful or objectionable content, undermining the safety measures to prevent such outcomes.

Addressing the challenge of securing AI models against these threats involves identifying and mitigating vulnerabilities that attackers could exploit. The task is daunting; it requires a nuanced understanding of how AI models can be manipulated. Researchers have developed various testing and evaluation methods to probe the defenses of LLMs and MLLMs. These methods range from altering textual inputs to introducing visual perturbations designed to test the models’ adherence to safety protocols under various attack scenarios.

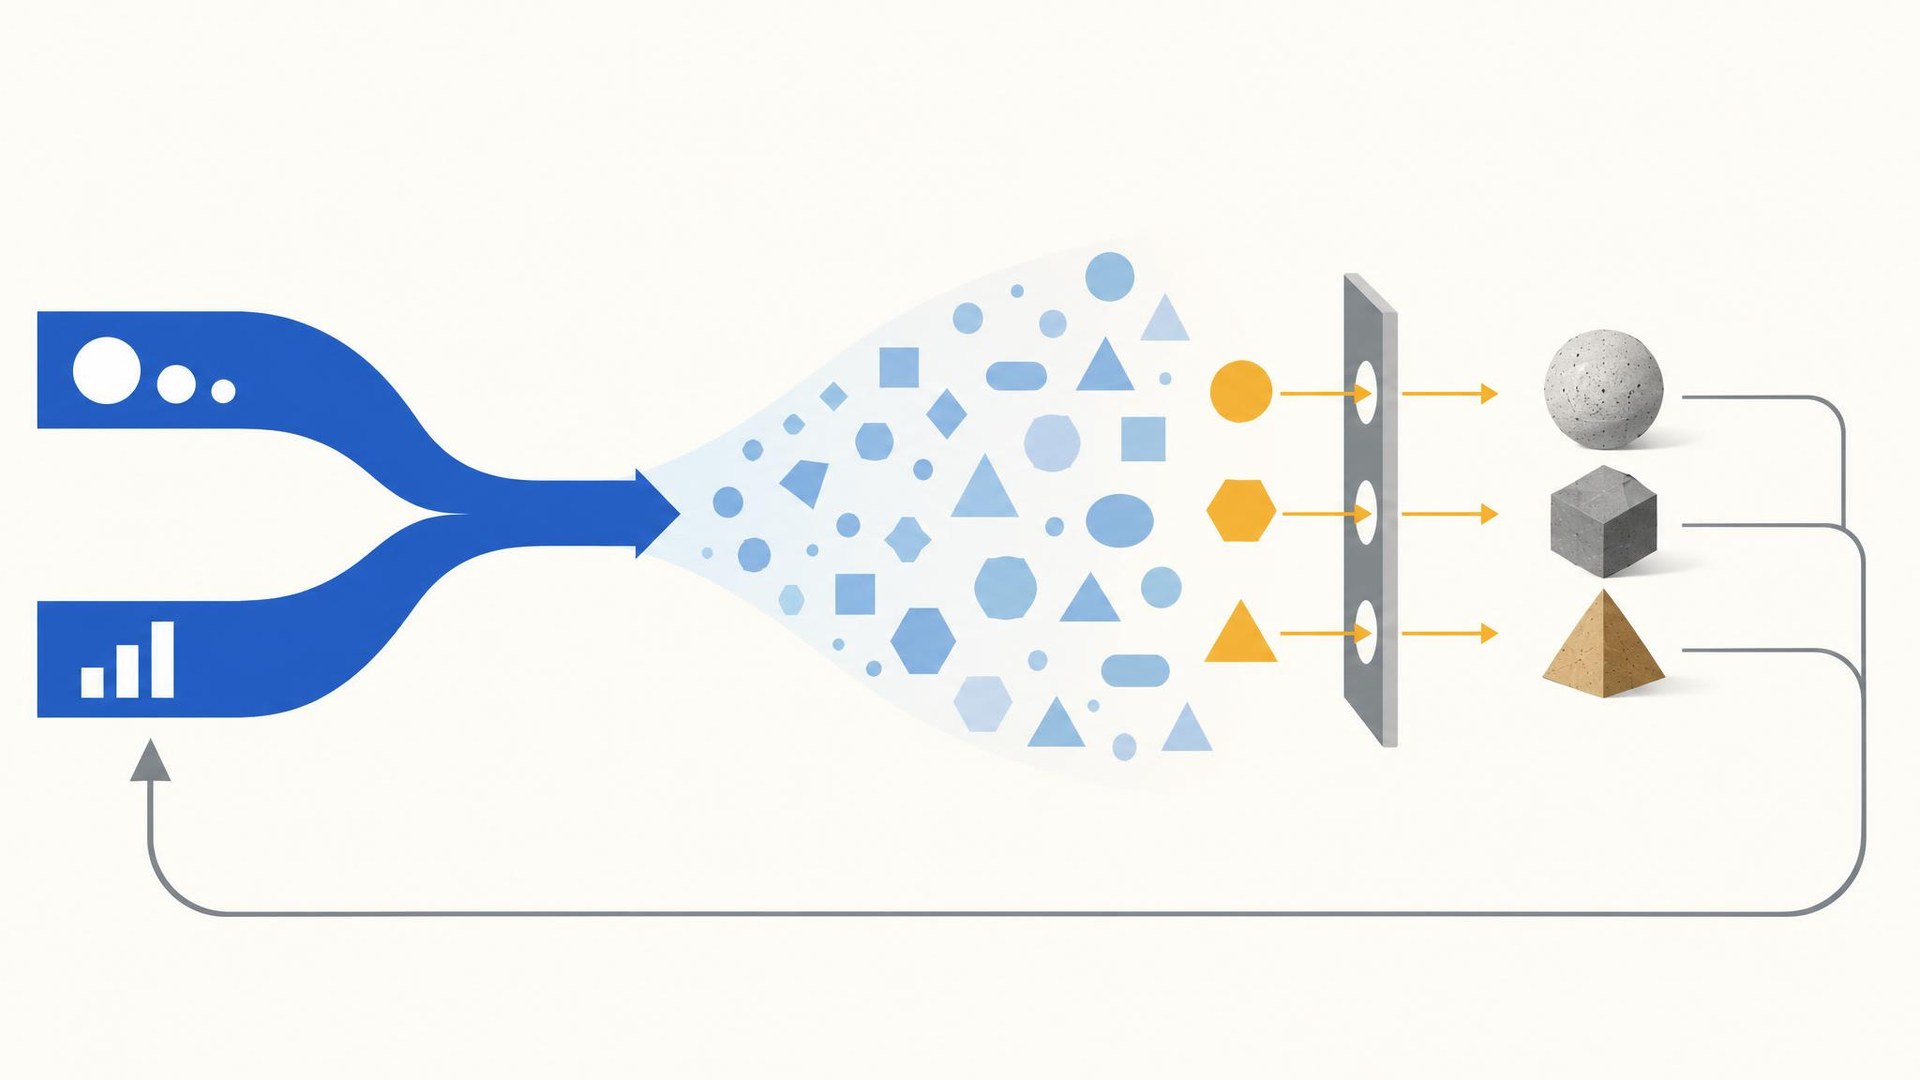
Researchers from LMU Munich, University of Oxford, Siemens AG, Munich Center for Machine Learning (MCML), and Wuhan University proposed a comprehensive framework for evaluating the robustness of AI models. This framework involves the creation of a dataset containing 1,445 harmful questions spanning 11 distinct safety policies. The study employed an extensive red-teaming approach, testing the resilience of 11 different LLMs and MLLMs, including proprietary models like GPT-4 and GPT-4V, as well as open-source models. Through this rigorous evaluation, researchers aim to uncover weaknesses in the models’ defenses, providing insights that can be used to fortify them against potential attacks.

The study’s methodology is noteworthy for its dual focus on hand-crafted and automatic jailbreak methods. These methods simulate a range of attack vectors, from inserting harmful questions into templates to optimizing strings as part of the jailbreak input. The objective is to assess how well the models maintain safety protocols despite sophisticated manipulation tactics.

The study’s findings offer insights into the current state of AI model security. GPT-4 and GPT-4V exhibited superior robustness to their open-source counterparts, resisting textual and visual jailbreak attempts more effectively. This discrepancy highlights the varying levels of security across different models and underscores the importance of ongoing efforts to enhance model safety. Among the open-source models, Llama2 and Qwen-VL-Chat stood out for their robustness, with Llama2 even surpassing GPT-4 in certain scenarios.

The research contributes significantly to the ongoing discourse on AI safety, presenting a nuanced analysis of the vulnerability of LLMs and MLLMs to jailbreak attacks. By systematically evaluating the performance of various models against a wide range of attack methods, the study identifies current weaknesses and provides a benchmark for future improvements. The data-driven approach, incorporating a diverse set of harmful questions and employing comprehensive red-teaming techniques, sets a new standard for assessing AI model security.

Research Snapshot

In conclusion, the study conclusively highlights the vulnerability of LLMs and MLLMs to jailbreak attacks, posing significant security risks. Establishing a robust evaluation framework, incorporating a dataset of 1,445 harmful queries under 11 safety policies, and applying extensive red-teaming techniques across a spectrum of 11 different models provides a comprehensive assessment of AI model security. Proprietary models like GPT-4 and GPT-4V demonstrated remarkable resilience against these attacks, outperforming their open-source counterparts.


Check out the Paper. All credit for this research goes to the researchers of this project. Also, don’t forget to follow us on Twitter. Join our Telegram Channel, Discord Channel, and LinkedIn Group.

If you like our work, you will love our newsletter..

Don’t Forget to join our 39k+ ML SubReddit

YOU MAY ALSO LIKE

What’s The Meaning Of The “A” On Your USB-A Ports?

Which Is Actually Better For Your Ears?

Hello, My name is Adnan Hassan. I am a consulting intern at Marktechpost and soon to be a management trainee at American Express. I am currently pursuing a dual degree at the Indian Institute of Technology, Kharagpur. I am passionate about technology and want to create new products that make a difference.


🐝 Join the Fastest Growing AI Research Newsletter Read by Researchers from Google + NVIDIA + Meta + Stanford + MIT + Microsoft and many others…


Credit: Source link

ShareTweetSendSharePin

Related Posts

What’s The Meaning Of The “A” On Your USB-A Ports?
AI & Technology

What’s The Meaning Of The “A” On Your USB-A Ports?

November 15, 2026
Which Is Actually Better For Your Ears?
AI & Technology

Which Is Actually Better For Your Ears?

November 15, 2026
Anthropic Targets .4 Trillion Valuation in Blockbuster IPO
AI & Technology

Anthropic Targets $1.4 Trillion Valuation in Blockbuster IPO

November 15, 2026
CoreWeave Boosts Forecast, Easing Slowdown Concerns
AI & Technology

CoreWeave Boosts Forecast, Easing Slowdown Concerns

November 15, 2026
Next Post
See aerial video of Baltimore bridge collapse

See aerial video of Baltimore bridge collapse

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

Search

No Result
View All Result
DuPont Partners with Microsoft and NobleAI on Agentic AI for R&D – Unite.AI

DuPont Partners with Microsoft and NobleAI on Agentic AI for R&D – Unite.AI

November 12, 2026
Russell Brand denies rape and sex assault charges

Russell Brand denies rape and sex assault charges

November 15, 2026
Suicides Raise Alarm Inside US Cybersecurity Agencies

Suicides Raise Alarm Inside US Cybersecurity Agencies

November 15, 2026

About

Learn more

Our Services

Legal

Privacy Policy

Terms of Use

Bloggers

Learn more

Article Links

Contact

Advertise

Ask us anything

©2020- TradePoint.io - All rights reserved!

Tradepoint.io, being just a publishing and technology platform, is not a registered broker-dealer or investment adviser. So we do not provide investment advice. Rather, brokerage services are provided to clients of Tradepoint.io by independent SEC-registered broker-dealers and members of FINRA/SIPC. Every form of investing carries some risk and past performance is not a guarantee of future results. “Tradepoint.io“, “Instant Investing” and “My Trading Tools” are registered trademarks of Apperbuild, LLC.

This website is operated by Apperbuild, LLC. We have no link to any brokerage firm and we do not provide investment advice. Every information and resource we provide is solely for the education of our readers. © 2020 Apperbuild, LLC. All rights reserved.

No Result
View All Result
  • Main
  • AI & Technology
  • Stock Charts
  • Market & News
  • Business
  • Finance Tips
  • Trade Tube
  • Blog
  • Shop

© 2023 - TradePoint.io - All Rights Reserved!