
























A threat advisory can reach a small utility in seconds. Deciding whether it matters—and what to do about it—can take far longer. Cyware is targeting that gap with Last Mile Agents, a new set of AI agents designed to turn shared cybersecurity intelligence into daily priorities for smaller organizations.
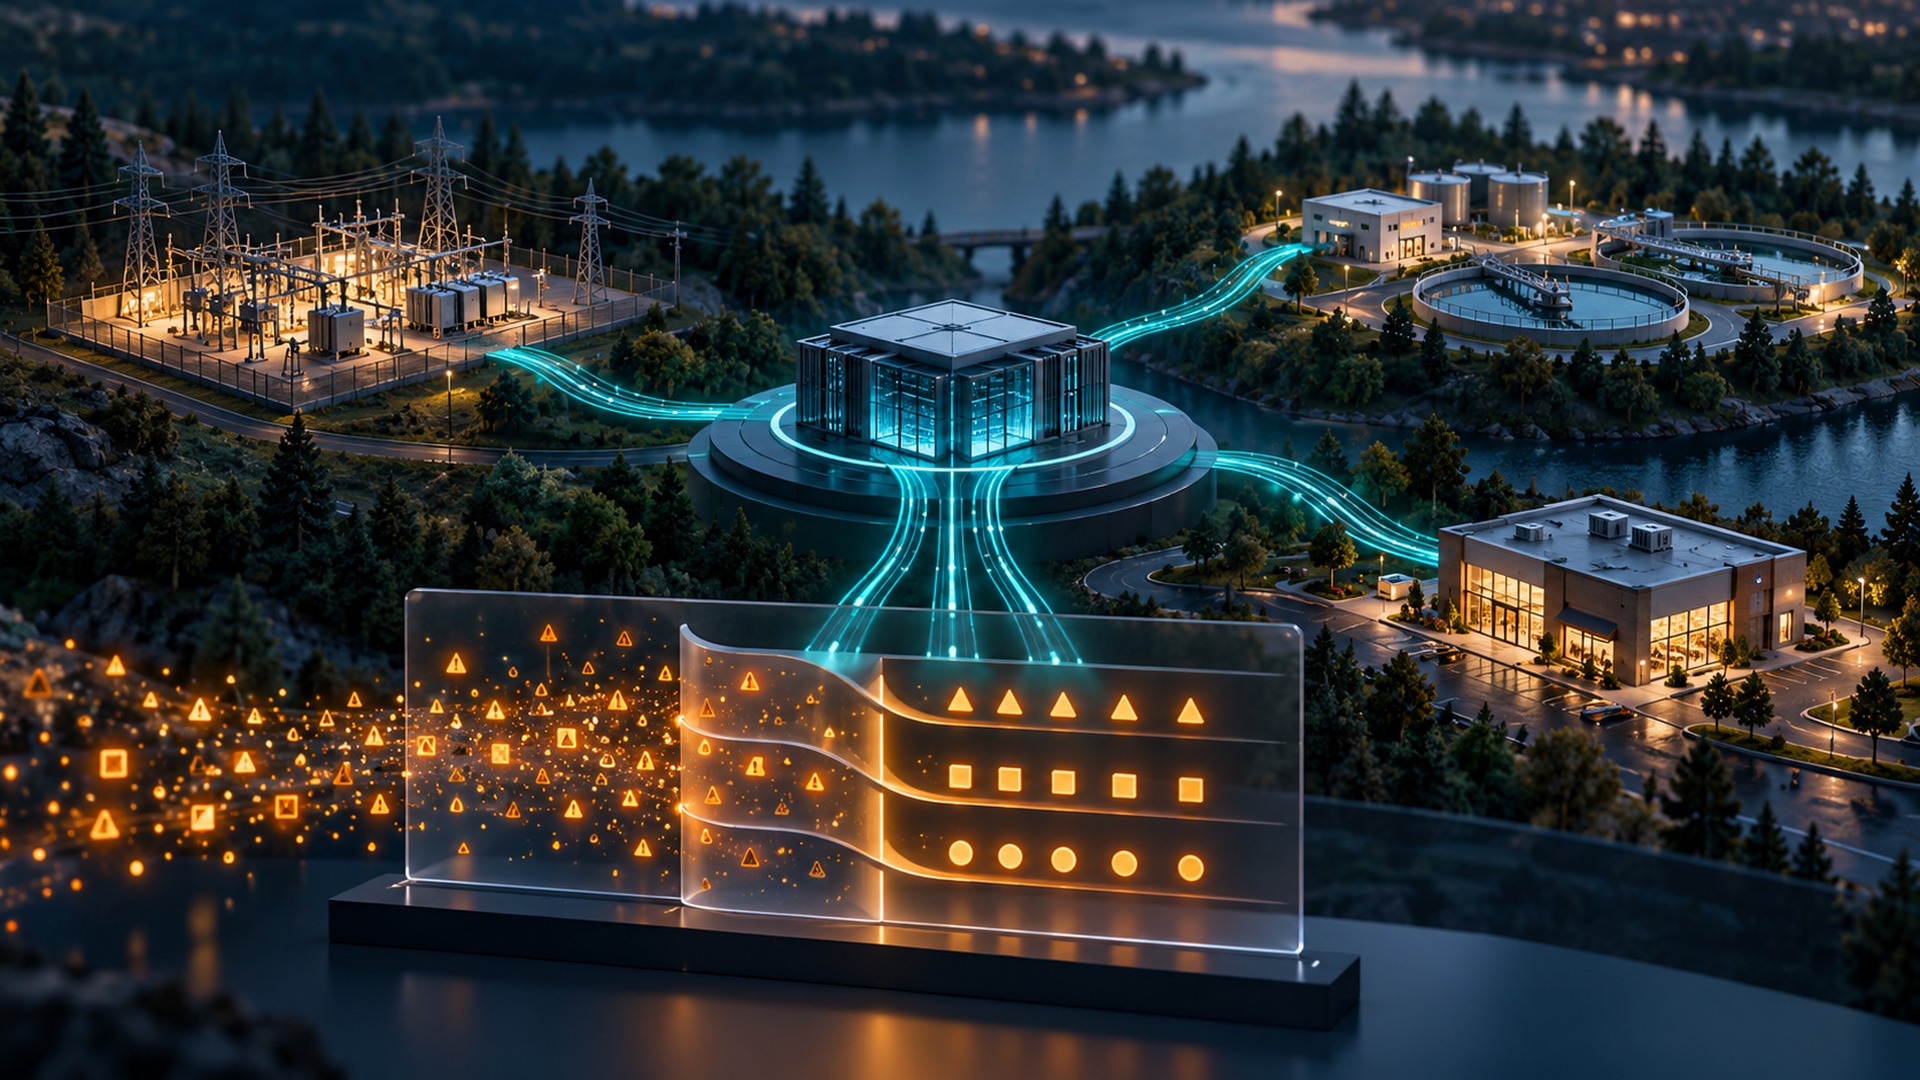
Announced on October 22, the agents are aimed at members of threat-sharing networks that receive advisories from community or state hubs but lack a dedicated threat intelligence team. Rather than giving every recipient the same reading list, Cyware says the agents assess incoming information against each organization’s sector, technology, and operating environment.
The initial release includes Vulnerability Watch and Threat Briefing, both supported by a Priority Intelligence Requirements agent. The immediate deliverable is prioritized guidance; automated actioning is part of Cyware’s plans for subsequent development.
Turning Shared Advisories Into Local Priorities
Threat-sharing networks help organizations pool information about vulnerabilities, attackers, and emerging campaigns. Their value, however, depends on what happens after an advisory arrives. A large enterprise may have analysts to compare that intelligence with its systems. A small business or cooperative utility may depend on a single security generalist who is also managing routine IT work.
Cyware’s approach separates the work of the intelligence hub from that of its members. The hub operates the Cyware platform and curates the intelligence. Connected member organizations use Last Mile Agents tailored to their priorities, without having to deploy the platform themselves, according to the announcement.
That distinction matters for adoption. The proposition is to make an existing sharing relationship more useful at its receiving end, rather than requiring each small organization to establish a full threat intelligence operation.
“Collective defense is only as strong as its last mile, and this is how we make it strong,” said Akshat Jain, Cyware’s CTO and co-founder, in the announcement. He said the agents begin with Priority Intelligence Requirements to capture what is relevant to each organization’s environment and apply that context to incoming advisories and vulnerabilities.
Three Agents, With Organizational Context at the Center
The Priority Intelligence Requirements, or PIR, Agent provides the foundation. It captures what matters to a member organization and continuously matches incoming intelligence against those requirements. In practical terms, this is intended to give the system a working definition of relevance before it ranks a threat.
- PIR Agent: Establishes the member’s intelligence priorities and uses them to assess arriving advisories and vulnerability information.
- Vulnerability Watch Agent: Produces a daily priority list organized into “act,” “attend,” and “track,” weighing exploitation activity and severity against the member’s environment.
- Threat Briefing Agent: Creates a daily ranked briefing that explains which developments deserve attention and why they matter to that member.
The distinction between severity and relevance is central to the design. A serious vulnerability is not equally urgent for every recipient of an advisory. An organization needs to understand whether the affected technology is part of its environment, whether exploitation is occurring, and how the issue compares with competing demands on its time.
How Last Mile Agents Fit Cyware’s Technology
The launch extends Cyware’s existing AI agent portfolio beyond analysts working at intelligence hubs. Its broader Agent Hub brings agents together within the company’s security products and describes controls for configurable autonomy, human oversight, authorization, and audit logging. Those platform capabilities provide context for Cyware’s strategy; the new release specifically describes member-facing prioritization and briefings.
Underneath that strategy is the problem of making disparate threat information usable. Cyware Intel Exchange supports ingestion, deduplication, enrichment, and normalization into STIX 2.1, a structured format for exchanging threat intelligence. It also links indicators, malware, campaigns, and threat actors, and maps adversary behavior to MITRE ATT&CK. These capabilities help explain the role of the hub: organizing intelligence before member organizations interpret it through their own priorities.
The company’s separate Cyware Orchestrate product connects security workflows through APIs, webhooks, and prebuilt integrations. It includes AI assistance for creating and troubleshooting playbooks. That is part of Cyware’s wider automation offering, but it should not be confused with the launch scope of Last Mile Agents: Cyware places automated actioning on the roadmap for these new agents.
The Test Is Whether Guidance Changes the Workday
For smaller security teams, a useful AI briefing needs to do more than compress a long advisory into a short paragraph. It needs to establish relevance, explain its ranking, and make the next decision easier. The quality of the organization’s stated requirements—and how well they stay aligned with its changing environment—will therefore be important to the agents’ practical value.
Cyware’s announcement does not provide performance benchmarks, pricing, or measured customer outcomes for Last Mile Agents. Its initial promise is narrower and concrete: give resource-constrained members a daily view of what matters most, using the intelligence their networks already distribute.
Vulnerability Watch and Threat Briefing are the first agents available, powered by the PIR Agent. Cyware is also offering a webinar on its AI agents. The broader opportunity is to make collective defense useful beyond the organizations that already have enough analysts to interpret it.
Credit: Source link