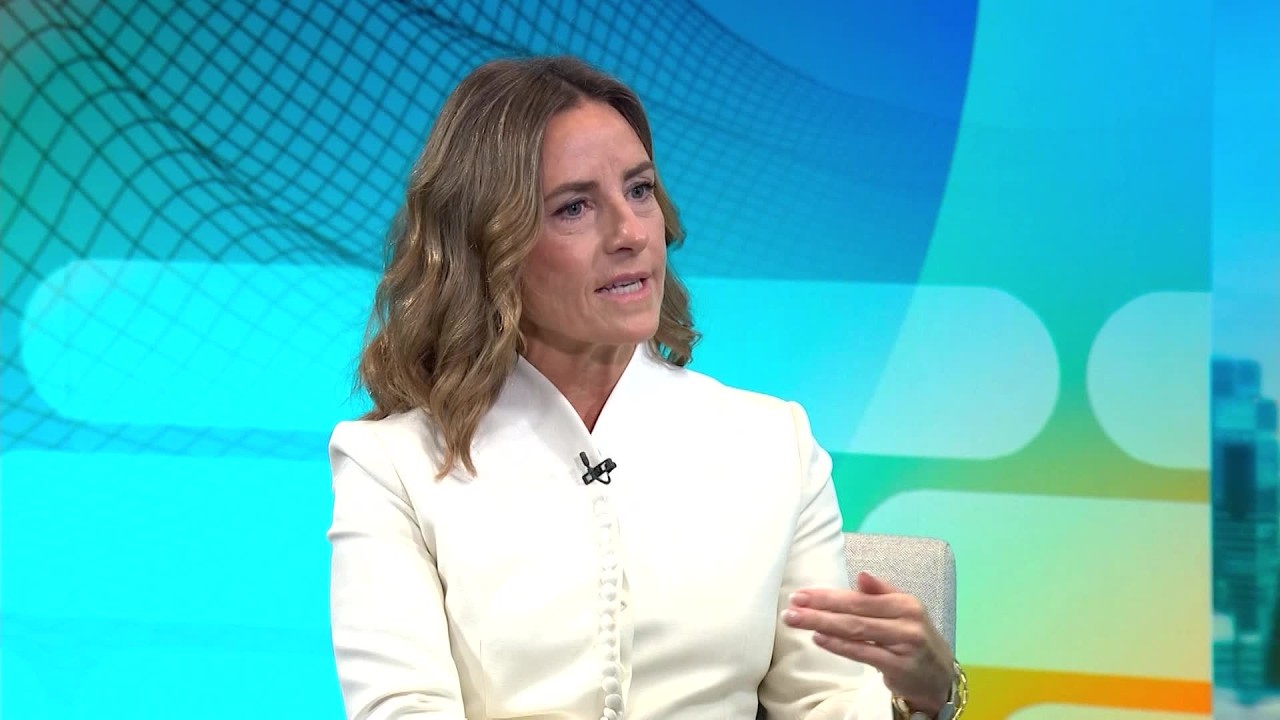



























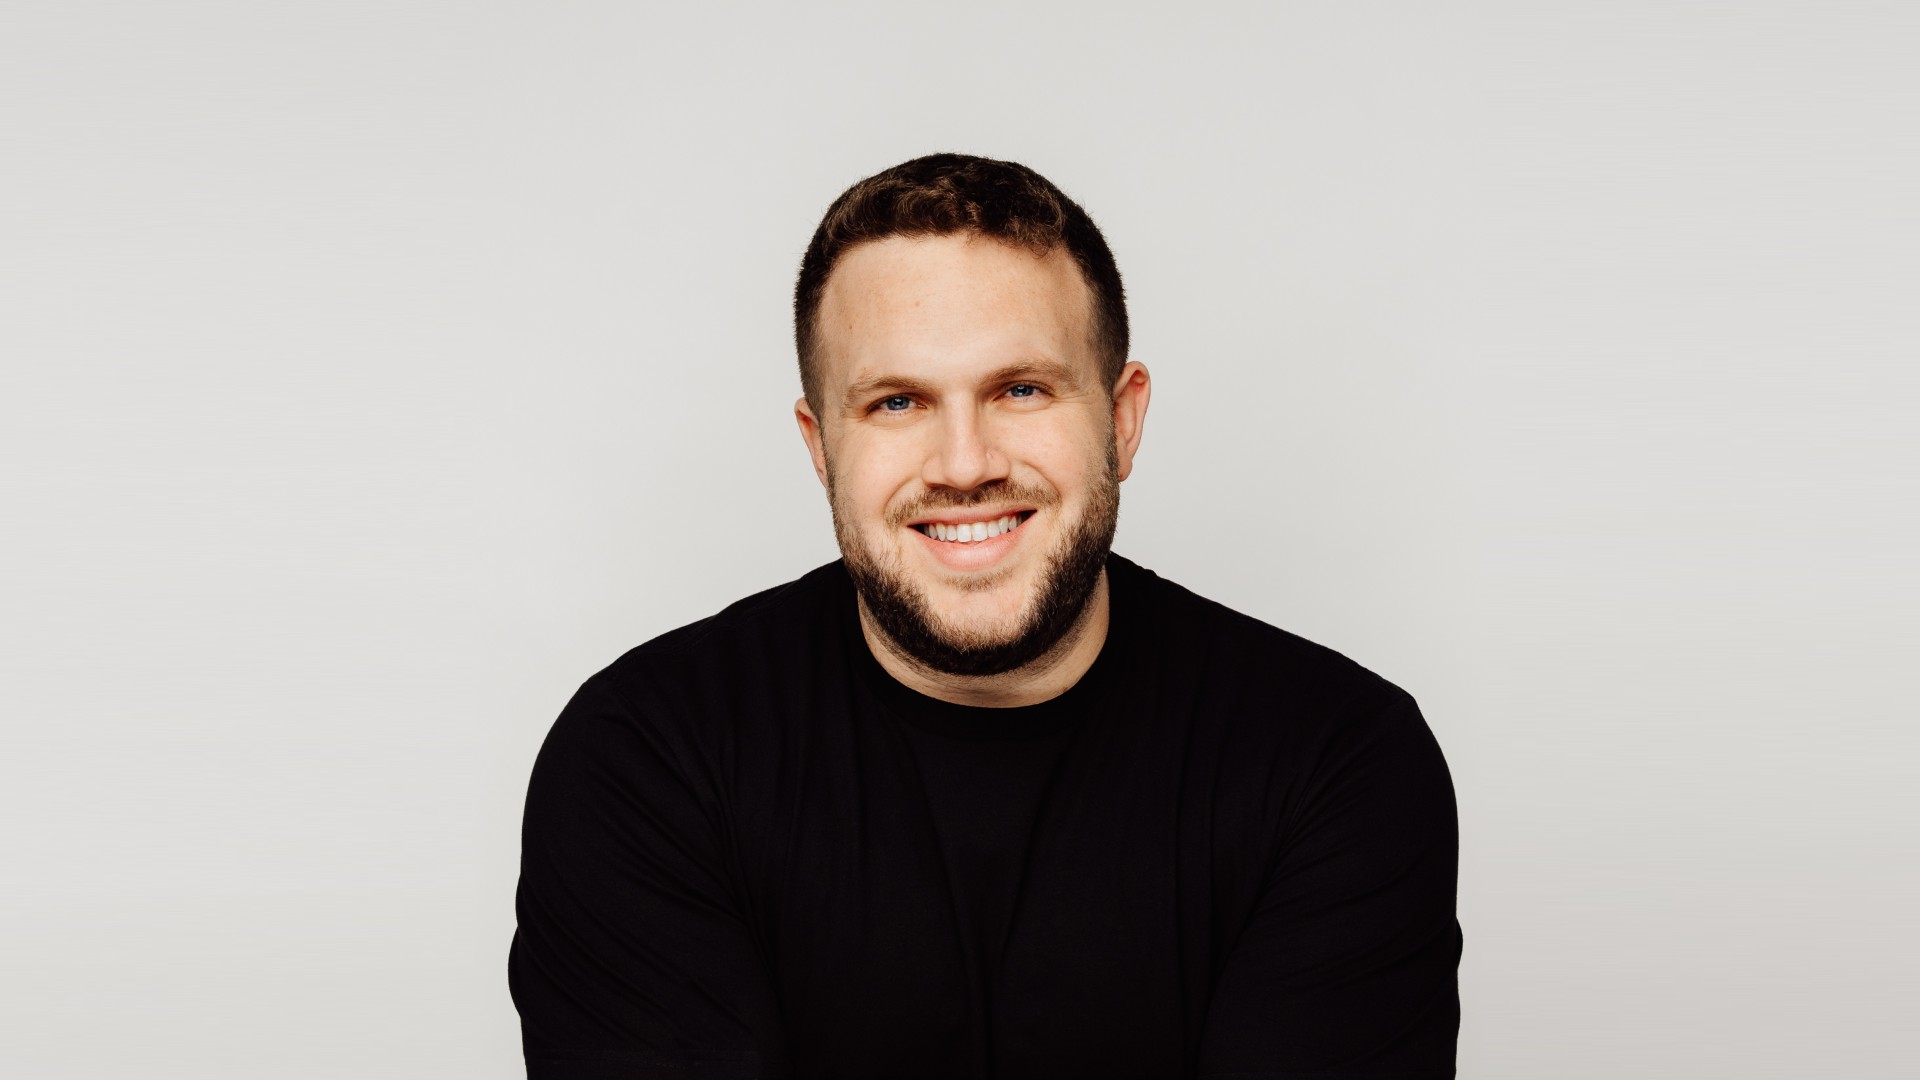
Alon Noy, CEO and Co-Founder of Astelia, is a cybersecurity leader with more than 15 years of experience spanning offensive and defensive security. He previously served in Israel’s Unit 8200 and went on to lead the Israeli National Cybersecurity Red Team, where his work included stress-testing critical infrastructure and collaborating with security teams on identifying and addressing real-world attack paths. Noy has also managed large research and development organizations, is a graduate of Israel’s Talpiot program, and holds an M.Sc. in Computer Science from Tel Aviv University. His experience operating from both the attacker and defender perspectives helped shape the approach behind Astelia, which focuses on determining which vulnerabilities are actually reachable and exploitable within an organization’s environment.
Astelia is an AI-native cybersecurity company focused on exposure and vulnerability management. Founded by veterans and former leaders of Israel’s National Red Team, the company uses AI and network-specific analysis to determine which vulnerabilities represent genuine attack paths rather than relying primarily on generic severity scores. Its platform maps an organization’s environment through read-only integrations, analyzes exploit requirements against network topology, and helps security teams prioritize vulnerabilities that are demonstrably reachable while identifying remediation options such as patching, configuration changes, segmentation, or compensating controls. The company’s broader goal is to help enterprises reduce the volume of vulnerability alerts they must investigate and focus resources on exposures that could realistically be exploited by attackers.
Before founding Astelia, you spent more than a decade in Israeli national security, including Unit 8200 and leading Israel’s National Cybersecurity Red Team, where you were tasked with thinking and operating like an attacker. What did those experiences teach you about how sophisticated attacks actually unfold, and what gap in the cybersecurity market ultimately led you to co-found Astelia?
For over a decade, my job was essentially to think like the person trying to break in, not the person trying to keep them out. The clearest lesson from that experience is that sophisticated attacks are almost never one dramatic hole in the wall. They’re usually two or three small things that nobody thought mattered on their own: an account that was never deactivated, a part of the network that was supposed to be isolated and wasn’t, a permission that was broader than it needed to be, and so on. When I led the National Red Team, we spent far more time understanding how a target’s network actually worked than we spent building the exploit itself. Once you know where the paths are, exploiting them is almost the easy part. When I moved to the defensive side, I started noticing a pattern. There was a long list of “critical” vulnerabilities with no real way to know which ones an attacker could actually reach. That’s the gap Astelia was built to close by taking reachability analysis, the process attackers use to find their way in, and putting it to work for defenders instead.
Astelia takes a different approach to vulnerability management by mapping an organization’s actual network topology and using agentic AI to determine which vulnerabilities are genuinely reachable and exploitable. How does this work in practice, and why do you believe traditional vulnerability scoring often gives defenders the wrong priorities?
We map an organization’s actual network, how systems really connect to one another and where existing network controls already stand in an attacker’s way, using read-only integrations. Once we have that picture, the AI works through each vulnerability and determines what it would actually take to exploit it, such as the access required, the path through the network, the conditions that would need to hold. It then checks all of that against the real topology and those existing controls. Out of everything a scanner flags, typically less than 1% turns out to be genuinely reachable. CVSS and EPSS both run into the same underlying problem: they score a vulnerability as though every network looks the same, as though the system were sitting exposed on the open internet, or as though industry-wide exploitation trends say anything about your specific environment. In most environments, neither assumption holds. A critical-rated bug three hops behind a segmented network isn’t the same risk as one sitting on a public-facing server, and a vulnerability with a high EPSS score industry-wide might not be reachable in your network at all. Those scores are fixed at a point in time and don’t reflect your network. Reachability changes constantly because networks, and the controls protecting them, do.
You’ve argued that much of what defenders worry about is irrelevant to how real attackers operate. From your experience conducting sanctioned attacks against highly secure environments, what do security teams most commonly misunderstand about the way attackers identify and chain together weaknesses?
There’s a common assumption that attackers go after whatever is rated most severe. In practice, we rarely do. We go after whatever gets us closest to the objective fastest, and that is often something the scanner had rated medium or low: a file share with the wrong permissions, credentials left over from a project that was supposedly shut down, a small foothold that only became dangerous once it was combined with something else nobody thought was related. Scanners evaluate findings individually. Attacks don’t work that way; an attacker is always looking at how things connect. Something that looks harmless on its own can be exactly what an attacker needs to move from a low-privilege account to full control. Most defenders are still set up to judge risk one finding at a time, and that’s why they keep missing the paths that actually matter.
AI is dramatically reducing the time and expertise required to turn newly disclosed vulnerabilities into working exploits. How does this change the economics of cyberattacks, and which types of attackers stand to gain the most from increasingly capable AI models?
The expensive part of building an exploit used to be expertise: finding the bug, working out exactly how to trigger it, making it reliable. What would often take months for a team of experts can now take hours for a common attacker with access to frontier models. That’s a genuine shift in the economics. Weaponizing a new CVE used to require real investment; now it barely does, and the time between a vulnerability being disclosed and a working exploit existing keeps shrinking. Most patch cycles were never designed to move at that pace. The attackers who benefit most from this aren’t the top-tier state actors, who already had strong offensive capabilities. It’s the smaller groups and opportunistic criminals who never had that kind of expertise in-house, and AI is effectively handing it to them.
The White House’s GOLD EAGLE initiative is built around closer cooperation between government, technology companies, and critical-infrastructure operators, with frontier AI being used to identify and remediate vulnerabilities faster. From an attacker’s perspective, what does this model get right, and where could it still fall short?
GOLD EAGLE correctly identifies how much time is wasted on duplicated effort, with different organizations independently scanning and triaging the same disclosed vulnerability before anyone actually acts. Centralizing that and applying AI to speed up coordination across government and infrastructure operators genuinely reduces the time an attacker has to work with, and from an attacker’s perspective, that’s the part that matters most. Speed is everything in this game. Where I think it falls short is that industry-wide coordination doesn’t tell any single company whether a particular vulnerability is reachable inside their own network. An organization can have access to a well-prioritized threat feed and still not know whether it applies to them. That final step, checking it against their own topology, remains each organization’s responsibility.
More than 100 technology, cybersecurity, financial, and infrastructure organizations have warned that there may be only a limited window to strengthen defenses before AI-enabled attacks become significantly more widespread. Do you share that sense of urgency, and what should organizations realistically accomplish during this “defenders’ window”?
I share that sense of urgency, though I’d frame the reason somewhat differently. AI-enabled attacks aren’t a future concern; the gap between a vulnerability being disclosed and a working exploit existing is already closing faster than most organizations can patch. Trying to win that race by patching faster alone isn’t realistic. What is realistic is using this period to understand one’s own environment. That means knowing the actual network topology, knowing which vulnerabilities are truly reachable, and focusing effort on that smaller set rather than spreading it across thousands of theoretical findings. It’s also worth using this time to build out remediation options beyond patching, such as segmentation or configuration changes, since patch velocity alone will not keep pace with AI-accelerated exploit development.
Collective cyber defense depends heavily on organizations sharing vulnerability and threat intelligence. What needs to change technically or culturally for governments and private companies to share useful information quickly enough to matter without creating new security risks in the process?
The technical challenge is the more solvable one. The harder problem is trust. No organization wants to disclose a weakness in its own environment and risk it being traced back to the organization, particularly if it later surfaces in a breach report. What works is sharing information that’s useful without being identifiable, the pattern of how something can be exploited rather than a description specific enough to point at one company. That requires better infrastructure, machine-readable threat data moving through automated channels rather than PDFs and mailing lists, but infrastructure was never really the obstacle. The obstacle is that sharing still feels like a legal liability to most organizations rather than something that protects them. A neutral, trusted intermediary, is part of what GOLD EAGLE aims to provide, and it could go a long way toward changing that.
Astelia emphasizes “reachability” rather than simply severity or the existence of a known exploit. As AI makes exploit generation faster and potentially more commonplace, does reachability become a more important measure of risk, and how should CISOs rethink vulnerability prioritization around that concept?
Reachability isn’t just becoming more important, it’s becoming the measure that actually determines Severity was always an approximation of how damaging something could be; reachability answers whether it can be exploited in your environment right now. Defenders used to bet that most low-severity findings could sit unpatched for months because nobody would realistically weaponize them. That assumption no longer holds once exploit generation is fast and cheap. has to shift from a severity-ranked backlog to eliminating exposures that are actually reachable. What separates the small number of vulnerabilities that matter from everything else is whether an attacker can reach them given your real network. CISOs should be asking for proof of reachability, not another score layered on top of CVSS.
Astelia is also applying AI agents to parts of the vulnerability lifecycle, from identifying new exposures to coordinating remediation. How much autonomy should cybersecurity agents ultimately have when they are capable of making changes to production environments, and where should humans remain firmly in the loop?
Agents should have real autonomy over analysis: mapping the network, working out exploit requirements, correlating new disclosures, surfacing what’s reachable. That’s where speed matters most, and an error just means a bad recommendation a human catches. I draw a firm line at unsupervised changes to production. Without network reachability data, an agent pushing a fix is guessing, and a bad firewall rule or segmentation change can do more damage than the vulnerability it was meant to close. That’s also why most of what gets marketed as “autonomous remediation” today is really auto-ticket creation. Enterprises want a human approving that kind of change, especially since a patch isn’t always available to begin with. The right model is agents that propose evidence-backed fixes with a person signing off before anything touches production. That will loosen as reachability data matures and trust builds in narrower, well-tested categories of change, but unsupervised action in production isn’t where I’d start.
Looking ahead, as both attackers and defenders gain access to increasingly capable autonomous AI systems, how do you expect the balance between offensive and defensive cybersecurity to change, and what will distinguish organizations that are prepared for that next phase from those that are not?
Attackers keep the early advantage with AI because they only need one working path, and AI is well suited to finding that path quickly: reconnaissance accelerates, exploit development accelerates, phishing content becomes more convincing. Defenders don’t close that gap by using AI to do the same things faster. They close it by using AI to discover and eliminate the vulnerabilities that are actually reachable in their own network, based on their own context, instead of managing risk against generic, industry-wide threat data. What will distinguish prepared organizations is whether they made that shift before it was forced on them, whether they can say, with evidence, which of their vulnerabilities are actually exploitable in their environment, rather than hoping their patch schedule keeps up. Organizations still managing risk in a generic context will keep getting caught out by something their own scanner rated low priority a year earlier.
Thank you for the great interview, readers who wish to learn more should visit Astelia.
Credit: Source link