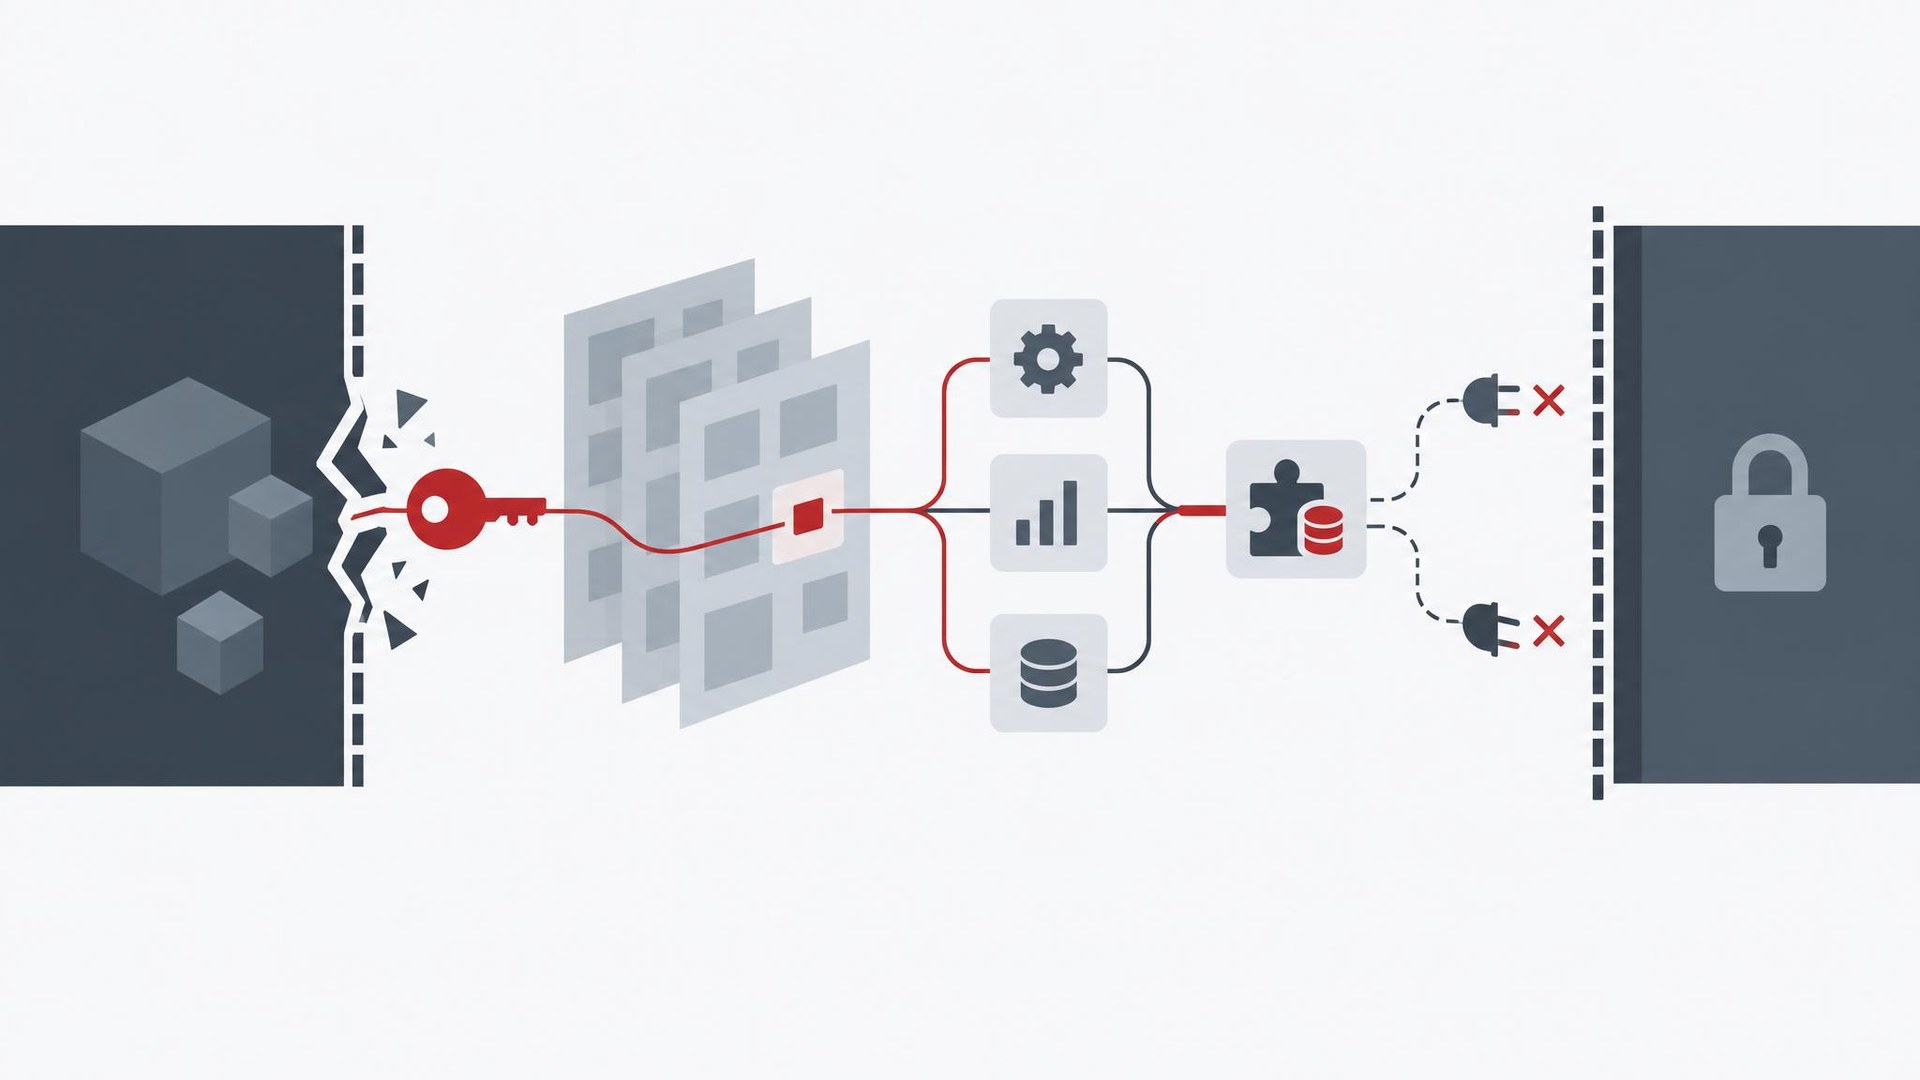

Cursor reported in an incident update published November 13, 2026 that an attacker used a Cursor-issued access key exposed by Fireworks AI to copy historical coding-agent traces and credentials, then reach select software tools used by Cursor and distribute malicious Claude Code extension builds. Less than 0.01% of customers had API credentials exposed.
Fireworks’ exposure of the key allowed data to be copied from a read-only bucket used for Cursor’s data sharing with the vendor. Its contents included limited coding-agent traces, mostly from 2025, from sessions not using Privacy Mode that Cursor was permitted to use for model training. A small number contained unredacted credentials, providing a route into select software-as-a-service tools used by Cursor.
From those tools, the attacker reached select archived, non-production Cursor source repositories, some containing business contact information. Other accessed material included limited support data and email conversations, product-usage metrics and contact details, summaries of some coding-agent conversations, and credentials users had sent to Cursor’s support team.
Affected Data and Unaffected Systems
Among users not using Privacy Mode, coding-agent traces were exposed for fewer than 0.05%, and Cursor said it identified and notified each affected user directly. The exposed traces were limited to storage used for historical offline analysis. Current customer data and live traffic, active inference requests, and Privacy Mode prompts and code were not affected.
Cursor also reported no impact to the production systems and infrastructure that run its service, or to customer code repositories. Official app updates and code shipped to clients and cloud services were unaffected: release code sits in a separate hosting system the attacker never accessed, and no release-signing keys were exposed. The company validated all other extensions in its VS Code marketplace and reviewed and rebuilt that store.
Extension Compromise and Containment
The update connects the intrusion to Cursor’s earlier malicious Claude Code extension disclosure. On October 29, 2026, the attacker used a credential stolen from the exposed internal data to put unauthorized builds directly on the cache serving Cursor’s VS Code extension marketplace. Anthropic did not publish them, its product was not vulnerable, and Open VSX, the marketplace source, never carried the malware. Cursor estimates that at most 5,000 users who requested specific cached versions potentially received a malicious build during approximately 11 hours of availability.
Cursor published indicators of compromise and remediation material on October 30, 2026, and began notifying affected users and team administrators through in-app messages and email. Administrators received lists of specific keys to rotate where credentials were exposed, and Cursor asked the issuing third-party services to revoke them. Customers whose support or business data may have been involved were notified directly.
Cursor’s monitoring systems identified the unauthorized activity. The company temporarily disabled more internal and product services than the evidence required as a precaution, disrupting certain features, and restored each after review. Cursor believes the incident is contained: the last attacker activity it observed occurred on November 1, 2026, and was blocked. Monitoring for anomalous activity continues.
Credential Revocation and Vendor Changes
Cursor moved all inference traffic off Fireworks, deactivated the vendor key and cut off Fireworks’ access to all datasets shared with it. Every exposed Cursor credential identified was rotated, followed by all credentials in use across internal systems as a precaution, even where there was no evidence of exposure. Cursor also expanded network restrictions across service providers where possible, added secret scanning to code repositories and other internal data sources, redeployed production infrastructure and engaged external forensics experts.
Separately, Fireworks AI’s own security bulletin reports that a third-party cloud provider hosting its research-and-development machines experienced an incident on October 23, 2026. An unauthorized party reached Fireworks development machines on October 24, 2026, and ran an unauthorized workload that led to additional customer-data impact; Fireworks detected the activity that day. It has not detected further successful unauthorized access on the customer platform since October 25, 2026. Those findings remain subject to an ongoing investigation.
Fireworks revoked and replaced credentials and service accounts, removed unnecessary elevated privileges, restricted network pathways, tightened storage and analytics access controls, and enhanced logging and monitoring with assistance from Palo Alto Networks Unit 42. It disabled self-serve dataset uploads and downloads used by Batch Inference and dataset-based training during the investigation. Training SDK remains available with zero data retention, meaning no training data is stored at rest, while Lab-based training operates in an isolated environment.
The new account places the marketplace compromise at the end of a chain that began with a vendor key and continued through credentials left in historical traces. That makes vendor-access revocation and broad credential rotation central to Cursor’s containment assessment, while Fireworks’ ongoing investigation leaves the vendor-side findings open to revision.
Credit: Source link